The short answer to what is WHOIS privacy: any arrangement that keeps a domain holder’s name, address, phone and email out of the public record. It once meant a paid add-on swapping in a provider’s details. In 2026 it also covers default redaction under GDPR and ICANN policy, and .si rules that publish only an email address for private individuals.
Two dates changed the picture for generic domains. ICANN’s WHOIS obligation ended on January 28, 2025, and its Registration Data Policy took effect on August 21, 2025. In anonymous RDAP lookups by BuySI Domains on October 22, 2026, only 2 of 20 high-profile domains showed the owner’s real organization.
What is WHOIS privacy: service, proxy or redaction
WHOIS privacy is any arrangement that keeps a domain holder’s personal contact details out of the public registration record. In 2026 it takes three forms. A privacy service shows a provider’s contact details while you stay the legal holder. A proxy service registers the domain in the provider’s own name and licenses it to you. Redaction is the default removal of personal fields that registrars apply under GDPR and ICANN policy.
ICANN’s 2013 Registrar Accreditation Agreement defines the first two in its specification on privacy and proxy registrations. A privacy service registers the name to its beneficial user and displays alternative contact details from the provider. A proxy service is itself the registered name holder and licenses the name to its customer, so the provider, not you, is the legal registrant.
Redaction is a policy, not a product. GDPR has applied since May 25, 2018, and ICANN’s Registration Data Policy now sets which fields go and which stay. Where redaction applies, Section 9.2.2 removes the registrant’s name, street, postal code, phone and fax, while Section 9.1 keeps the country public, plus state or province if collected.
GDPR protects natural persons only, and its Recital 14 excludes a legal person’s name and contact details. ICANN still lets registrars treat company records like private ones, because distinguishing legal from natural persons is optional (Section 9.2.1). That is why a listed company’s .com can look as anonymous as a hobby blog.
When a privacy or proxy service is in place, Section 9.2.5 requires the registrar and registry to publish the service’s full data. At most gTLD registrars, a paid add-on no longer decides whether your data is public; it decides whose name fills the record.
How WHOIS became RDAP
WHOIS is no longer the required lookup for generic domains such as .com. ICANN’s 2023 Global Amendments ended the obligation of gTLD registries and registrars to run WHOIS on port 43 and the web on January 28, 2025. RDAP, a structured JSON protocol, became the required service. The old servers did not all switch off: Verisign’s .com WHOIS still answered our query on October 22, 2026.
RDAP, the Registration Data Access Protocol, returns machine-readable records with explicit markers for redacted fields. It can also show more data to authenticated users than to anonymous ones. According to the IETF, 74 gTLD registries shut down their WHOIS services in February 2025, and RDAP queries overtook WHOIS queries in June 2025.
| Date | Change | Applies to |
|---|---|---|
| May 25, 2018 | GDPR applies; ICANN’s Temporary Specification (adopted May 17, 2018) takes effect | EU personal data; gTLDs |
| August 7, 2023 | Global Amendments take effect and require the gTLD RDAP Profile | gTLDs |
| January 28, 2025 | WHOIS obligation ends; RDAP is the required service | gTLDs |
| June 2025 | RDAP queries pass WHOIS queries, per the IETF | Lookup traffic |
| August 21, 2025 | Registration Data Policy replaces the interim rules | gTLDs |
None of this binds country-code domains directly. ICANN’s policy covers gTLD registries and accredited registrars, while ccTLD registries such as those for .ai and .si set their own publication rules. In the EU, NIS2 Article 28 adds a legal floor: accurate registration data, publication of non-personal data without undue delay, and answers to lawful, substantiated access requests within 72 hours.
What a public lookup shows: .com, .ai and .si compared
To see what these rules produce, BuySI Domains ran anonymous RDAP lookups on October 22, 2026, for 20 high-profile domains: 6 .com, 6 .ai and 8 .si. For the .si names we also ran port-43 WHOIS queries. We recorded only which fields appeared, never personal content. The sample covers famous names, mostly at brand-protection registrars, so read it as a snapshot, not a statistic.
The domains were google.com, apple.com, nytimes.com, stripe.com, github.com and openai.com; character.ai, perplexity.ai, x.ai, claude.ai, lovable.ai and mistral.ai; and arnes.si, register.si, rtvslo.si, 24ur.si, siol.si, mkr.si, essai.si and netserver.si. Three of the .si names are on BuySI Domains’ own list and returned the same output as the rest.
| Field in anonymous lookup | .com (6 domains) | .ai (6 domains) | .si (8 domains) |
|---|---|---|---|
| Registry record lists contacts | No (thin registry) | Yes | No |
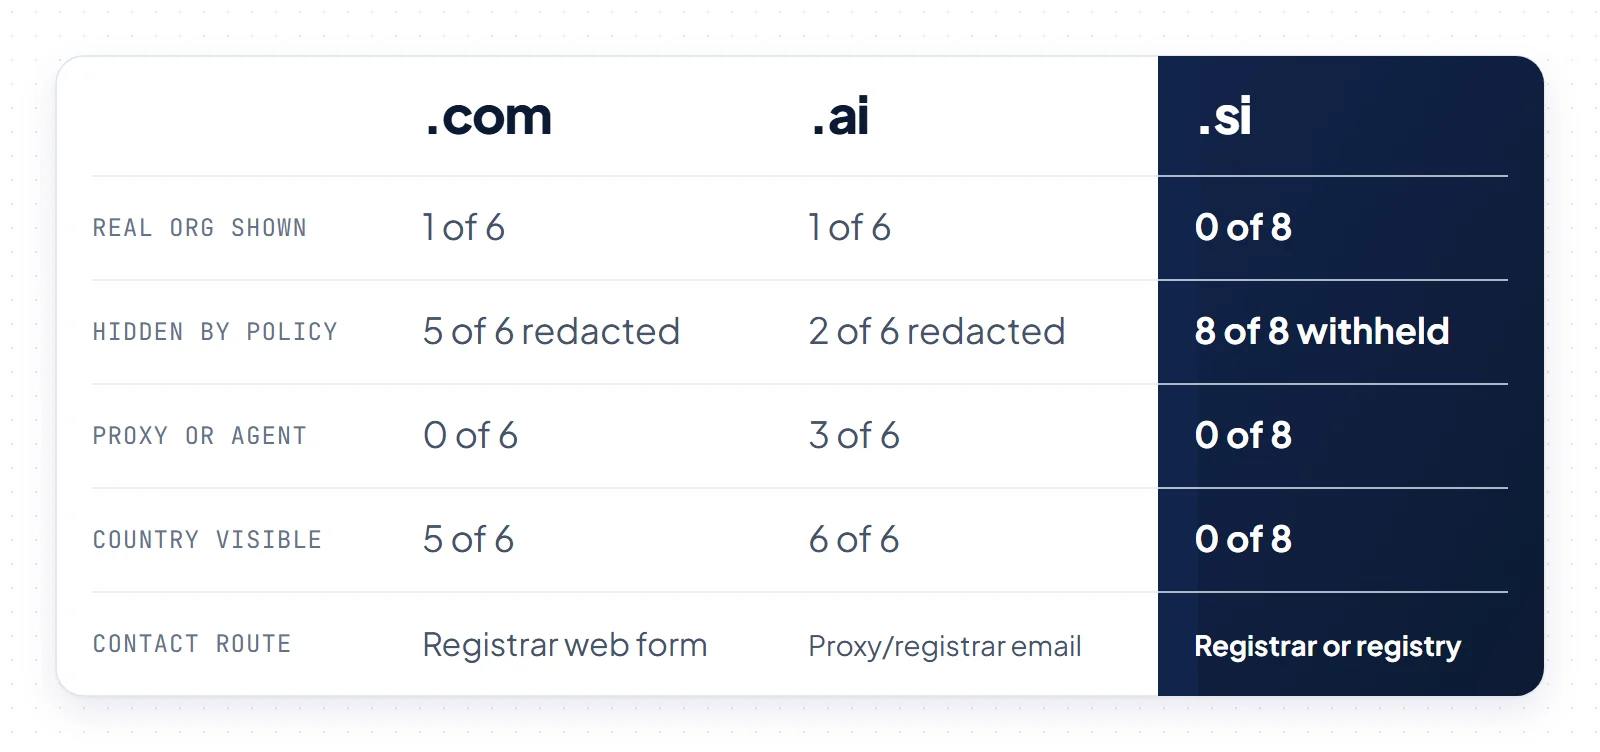
| Owner’s real organization shown | 1 of 6 | 1 of 6 | 0 of 8 |
| Name and organization redacted or withheld | 5 of 6 redacted | 2 of 6 redacted | 8 of 8 withheld |
| Privacy service or agent shown instead | 0 of 6 | 3 of 6 | 0 of 8 |
| Registrant country visible | 5 of 6 | 6 of 6 | 0 of 8 |
| Main contact route | Registrar web form (4 of 6) | Proxy or registrar email (4 of 6) | Registrar or Register.si request |
In anonymous RDAP lookups by BuySI Domains on October 22, 2026, only 2 of 20 high-profile domains showed the owner’s real organization: nytimes.com and claude.ai. Five of six .com records redacted name and organization. Three of six .ai records showed a privacy service or agent instead of the owner, and all eight .si records withheld holder data. A registrant country appeared in 11 of 12 .com and .ai records, although in three .ai records it was the proxy’s or agent’s country.
A .com lookup takes two steps. Verisign runs .com as a thin registry. Its record names only the registrar and links to the registrar’s own RDAP server, which holds the contact data. Our guide to how registrars and registries split the work explains why. The record for stripe.com returned an empty registrant object, the only one of the 12 .com and .ai records without a country.
The .ai records look more open, but the names they show often belong to someone other than the owner. Two showed Domains By Proxy, LLC, and x.ai showed DNStination Inc., a third-party organization rather than the company behind the site. Both redacted .ai records were registered through Cloudflare, while the registry showed full contact data for the other four. The redaction therefore appears to come from the registrar or a privacy service rather than the registry.
How .si handles holder data
For a .si domain held by a natural person, Register.si publishes only an email address. .si is Slovenia’s country-code domain. For AI companies it reads as SuperIntelligence. The registry, operated by the Slovenian academic network Arnes, follows its own terms and Slovenian law rather than ICANN’s gTLD policy.
Section 13.3 of the registry’s General Terms (version published November 15, 2024) says that for a natural person only the email address appears in WHOIS. Section 13.4 requires registrars to tell natural persons that they can publish a special-function email address, unrelated to any personal data, instead of their personal one. Other details appear only at the holder’s request.
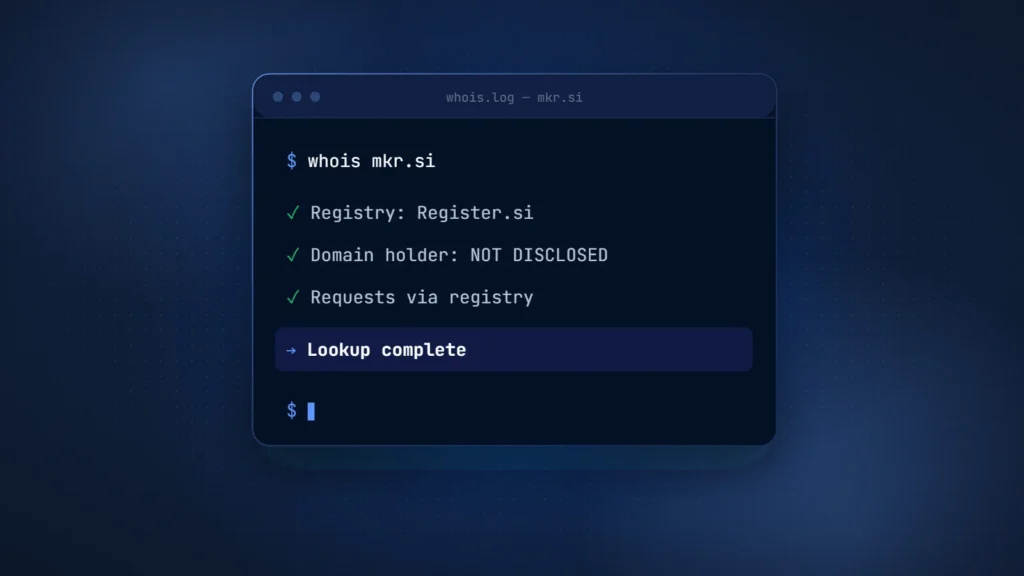
Our lookups showed even less. Anonymous RDAP and port-43 lookups showed no holder data for any of the eight .si domains we checked on October 22, 2026. That included the domains of Arnes and the broadcaster RTV Slovenija. Port 43 returned “NOT DISCLOSED” for the holder and the technical contact. RDAP marked each record as truncated by server policy. Register.si’s RDAP page states that anonymous users see no holder information.
Register.si’s data policy says holder information for legal entities is public. The port-43 output points to the registry’s web lookup for full details. We did not test that web lookup, so this guide makes no claim about what it shows.
The .si terms describe no privacy or proxy option, and holders must keep their data accurate and current (Sections 6.1.1 and 8.1.1). Under Sections 11.6 and 11.7, third parties can obtain holder data with the holder’s consent, on an official body’s binding decision, at a dispute arbiter’s request, or on a justified request. A justified request goes on the registry’s form. It must explain its grounds, prove that a court, administrative, arbitration or ADR procedure has started, and include a declaration accepting criminal and civil liability for misuse.
The registry’s disclosure page names trademark owners filing an ADR complaint and courts as typical requesters. It rules out requests for direct marketing. For eligibility and the rest of the registry’s rules, see our complete guide to the .si domain.
How to contact a hidden owner before you buy
Redaction hides a domain owner’s details, not the owner. When a gTLD registrar redacts the registrant’s email, it must publish a substitute contact route. Section 9.2.3 of ICANN’s Registration Data Policy requires an email address or web form that reaches the registrant without revealing who they are. In the .com sample checked by BuySI Domains on October 22, 2026, four of six records offered a registrar web contact form. For three of them, it was the only published way to reach the registrant.
With a privacy or proxy service, write to the service’s published email address. For .si there is no relay in the public record. Contact the registrar shown in the lookup and ask whether it will forward a message. If you have legal grounds, such as a trademark claim, file a justified request with Register.si. Its terms ask for proof that a court, administrative, arbitration or ADR procedure has started. An interest in buying is not among the grounds the registry lists.
If you need the data itself for a dispute, ICANN’s policy gives gTLD registrars 2 business days to acknowledge a disclosure request and 30 calendar days to answer it (Section 10.5). The request must state your identity, the data you want and the legal basis.
Hidden data changes how you approach buying a domain that is already taken. You may not know whether the person replying is the owner, a broker or a privacy service. Ask the seller to prove control, for example by adding a DNS record you specify. Then check the domain’s ownership and content history before you make an offer, and pay through a domain escrow service that releases funds only after the transfer completes.
Limits and downsides of WHOIS privacy
Domain privacy hides your details from the public record, not from your registrar. Registrars and registries still collect your real data, EU registries must verify it under NIS2, and both release it on justified requests. Fake contact details are no substitute: .si holders must keep their data accurate, and the registry may delete a domain for breach.
Some extensions do not allow privacy at all. The usTLD Privacy Services Policy bars registrars and resellers from offering anonymous or proxy registrations for .us domains, so .us registrant data stays public.
Relay addresses and web forms help only if someone reads them, so renewal notices, transfer requests and purchase offers can go unnoticed.
Which option fits your domain
For a private individual with a gTLD such as .com, default redaction at most registrars already removes name, street and phone. A privacy add-on mainly changes whose name fills the record, so check that its forwarding address reaches an inbox you read.
For a company, publishing the organization is a reasonable choice. ICANN’s policy requires registrars to tell holders that the organization is published only if they agree, and to publish it once they do (Sections 6.6 and 9.2.6). A visible owner is also easier to verify and to reach. A .si holder who is a natural person already gets an email-only record, so ask your registrar about the special-function address. Buyers should plan for a relay or registry request, not a phone call.